Export logs without exposing secret tokens
Export logs without exposing secret tokens
Protect support files without losing traceability
Choose where editing happens, which copy becomes the controlled record and when that record is locked. A Windows workstation crashes, and the support team needs logs that explain the failure without revealing customer data or account credentials. Design the workflow so that raw, edited and retained versions are not mistaken for one another.
Separate active work from archive
Create distinct intake, working, reviewed and retained states for Event Viewer exports, diagnostic CSVs, minidump archives, system information reports and reproduction screenshots. Avoid editing the only recoverable original inside a time-sensitive handoff. Lock the maintained archive when it is no longer actively being edited.
Choose a protection mechanism
For controlled local storage, Folder Lock documents encrypted lockers. That is different from its non-encrypting folder-hiding feature. Record which one was selected and why. Test a harmless sample on the actual supported Windows version before moving the real Windows diagnostic evidence records.
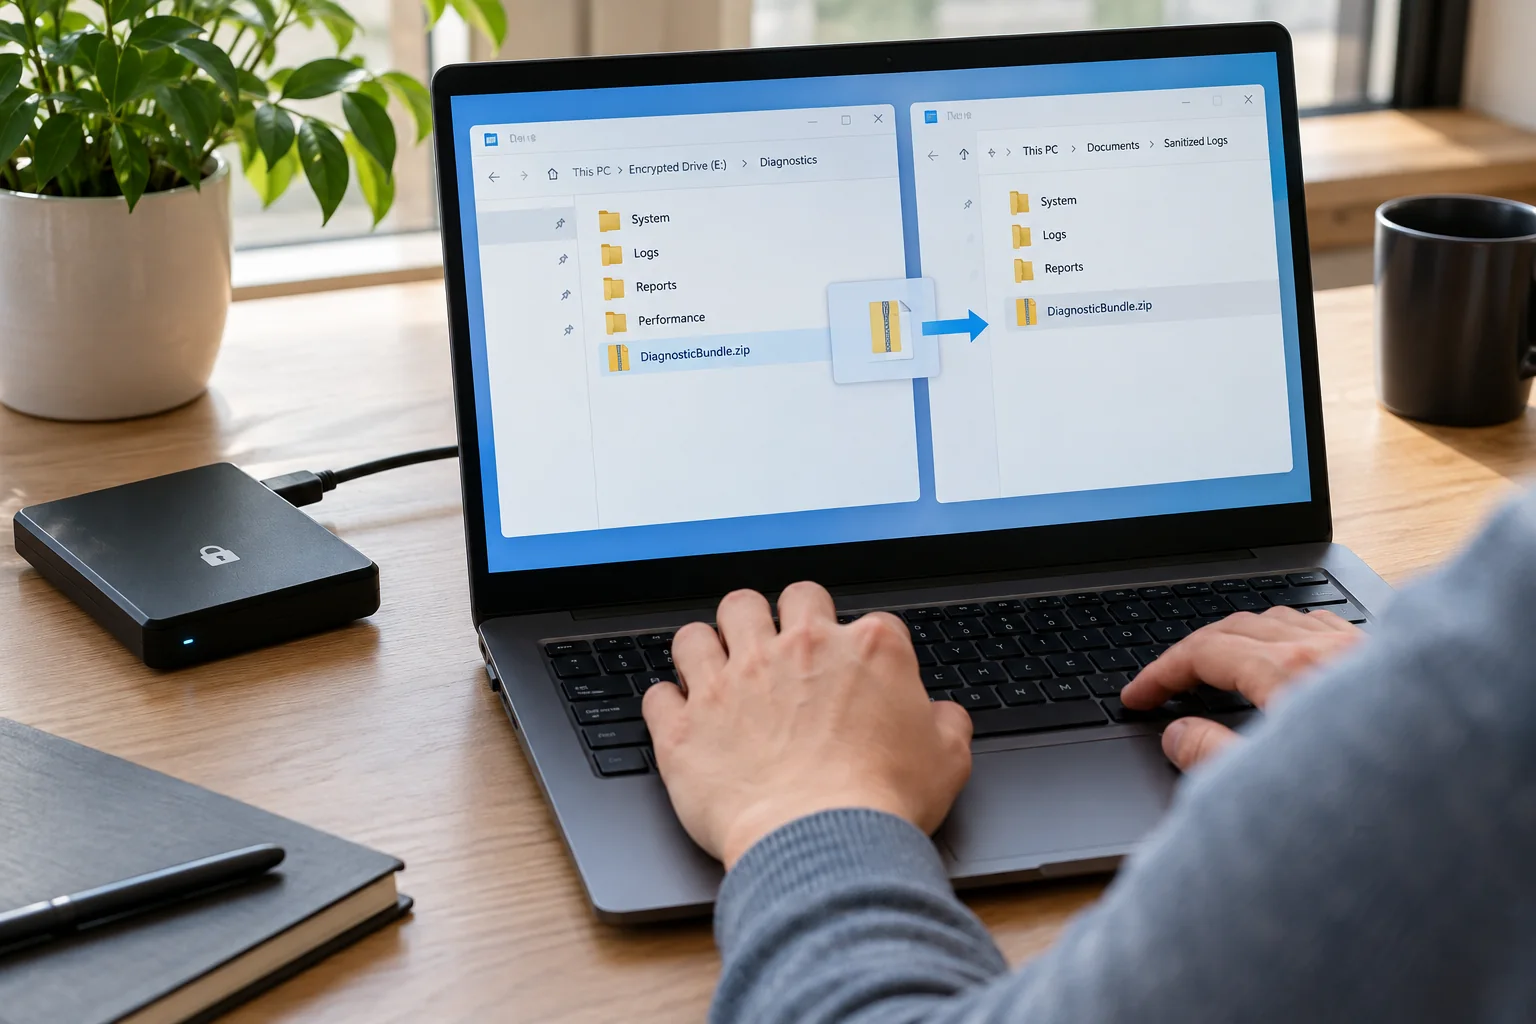
Verify the authorized workflow
Have the assigned support case owner and a designated security reviewer confirm they can find an authorized item, add an approved new version and lock or close the collection without exposing a decrypted desktop copy. Backups must be secured independently of the local locker.
Working-state example: diagnostic CSVs is edited in a limited-access workspace, checked for unintended copies, then entered into the approved encrypted archive as a named revision.
Practical implementation checklist
- Identify the accountable approver for Windows diagnostic evidence and write down the exact event being protected.
- Choose a non-sensitive sample drawn from the same format as Event Viewer exports; never use a real identity, key or patient record in a public example.
- Compare the unprotected working copy, restricted recipient copy and intended retained copy. Confirm where extra versions are created.
- Record the approved destination, any failed test, and a date for reassessing the workflow when personnel or software changes.
Questions readers should resolve
Is hiding a folder equivalent to encrypting it?
No. Concealment and encryption are different protections; check which feature was actually used. For Windows support artifacts, this means checking minidump files, handling trace tokens separately, and using a fake Event Viewer export as the review example. Maintain a small example that is easy for the owner to lock, reopen, close and recover without credentials from a real user.
Who should approve this Windows diagnostic evidence workflow?
Assign a named owner. In this context, start with the assigned support case owner and a designated security reviewer and confirm the applicable organizational authority.
Research and documentation
These sources support the technical boundaries described here. They are not substitutes for testing the current software on the target device, checking legal requirements, or independently confirming product claims.
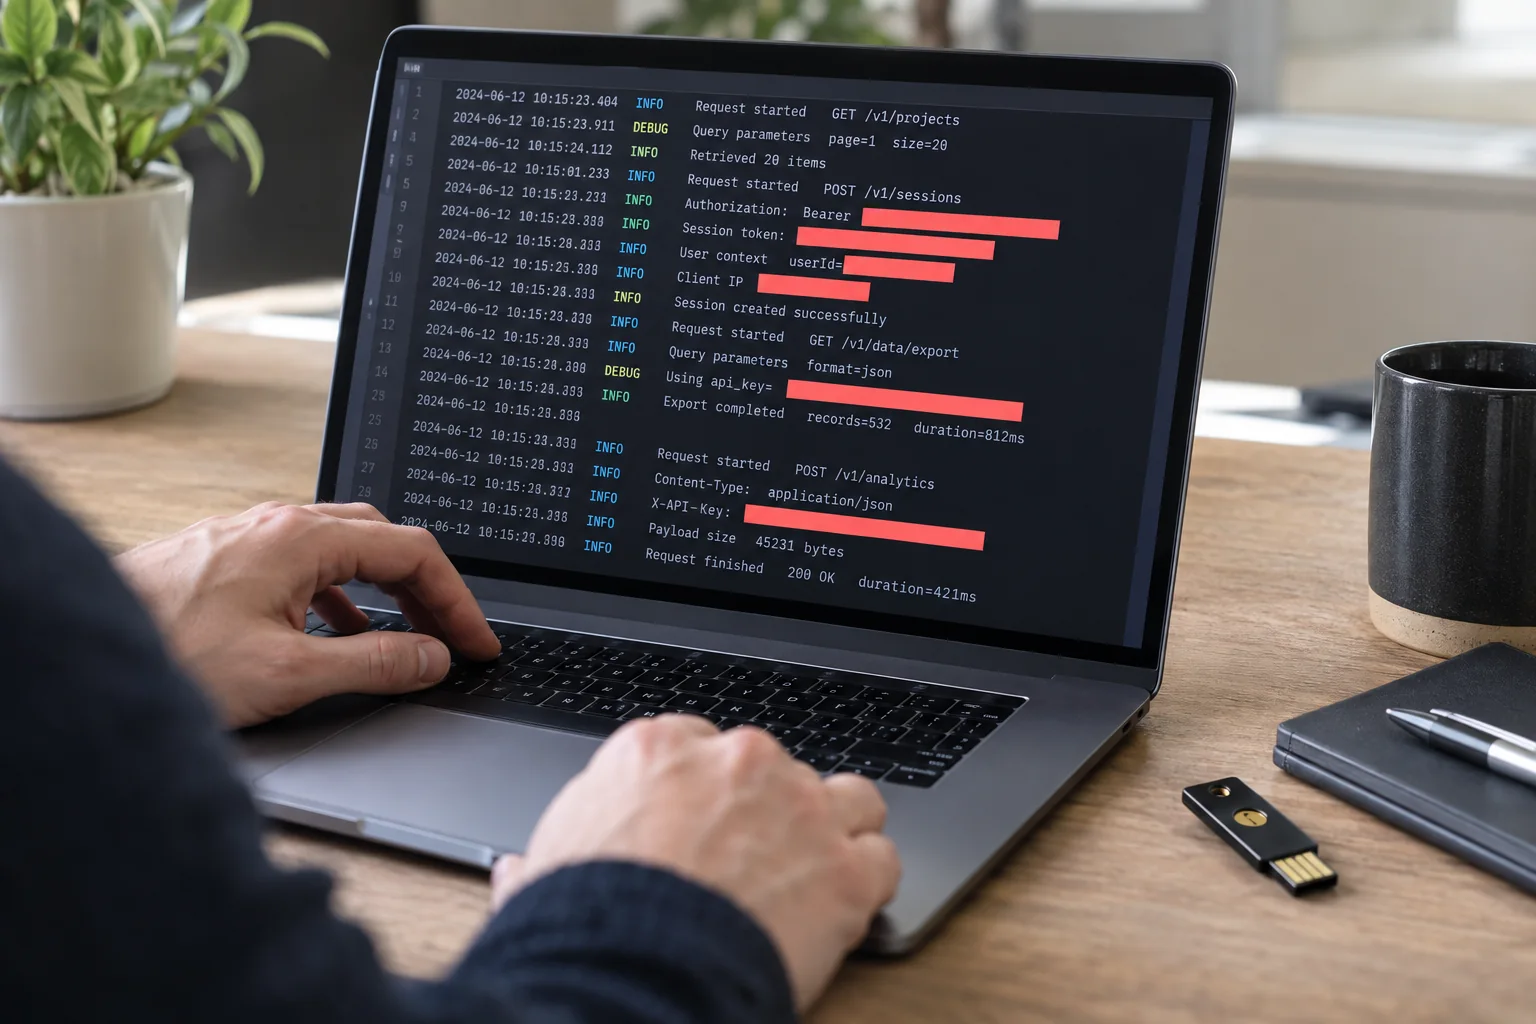
- Microsoft: Diagnostic Data Viewer
- NewSoftwares Folder Lock: documented features
- Folder Lock FAQ and lost-password limitations
Editorial note: No paid link placement is required for this guide. Product information, if mentioned, describes one possible tool and should not be read as an endorsement or an assertion of universal compatibility.